SMARTY: Transparently Securing Communications
In confidential computing, data can be protected while in use, in transit, and at rest. This protection is policy-controlled and can be enabled declaratively to encrypt network communications, ensuring that only the communicating parties can read the traffic. SMARTY investigates how this approach can support the declarative definition of a Software Defined Perimeter.
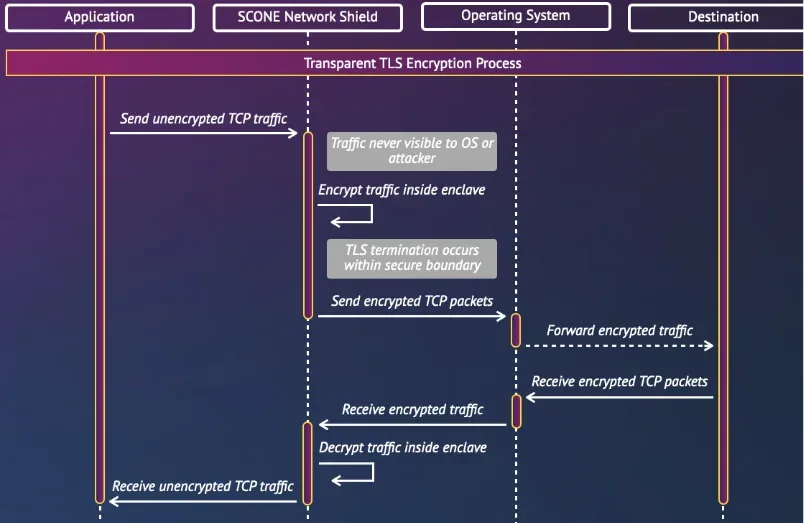
The SCONE Network Shield transparently encrypts TCP connections without modifying applications, including legacy services that do not support TLS. It operates between the application and the operating system, supports virtual enclaves based on Intel TDX and AMD SEVand integrates with SCONE’s attestation service to verify enclave residency, authenticate endpoints using TLS and provide supporting certificates.
As part of SMARTY, the SCONE Network Shield is further improved based on challenges encountered in production environments, with particular attention to network event handling. Further work will address the remaining limitations, including support for disconnect signals and message inspection.
Follow SMARTY for updates:
LinkedIn: https://www.linkedin.com/company/smartyeu/?viewAsMember=true
Website: https://www.smarty-project.eu