SMARTY’s Approach to Secure Confidential Deployments
Deploying confidential applications in Kubernetes environments requires ensuring that sensitive configuration and secrets are only accessible to trusted workloads. SMARTY is developing a confidential deployment approach that addresses this challenge without relying on Kubernetes administrators.
The solution automatically separates Kubernetes configuration from sensitive data. Configuration files are sanitized, while secrets are securely encrypted and released only after the application has successfully passed attestation.
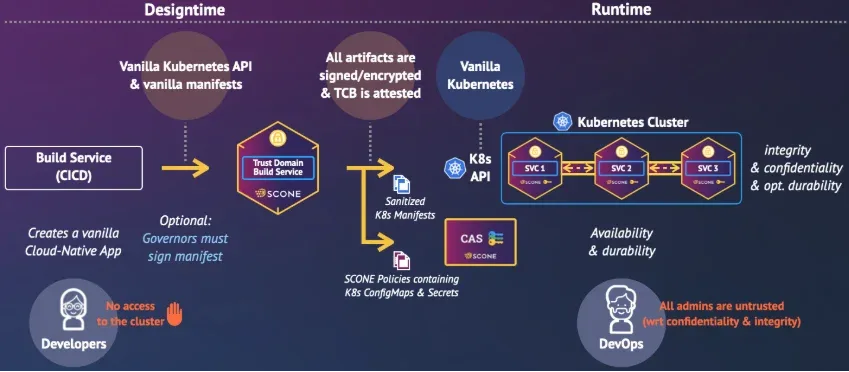
Integrated into the CI/CD pipeline, this approach enables confidential applications to be securely deployed even in untrusted or outsourced Kubernetes environments, protecting sensitive data throughout the deployment process.
Follow SMARTY for updates:
LinkedIn: https://www.linkedin.com/company/smartyeu/?viewAsMember=true
Website: https://www.smarty-project.eu